What are the best Bifrost alternatives in 2026?

Nolan Sullivan
Published · Updated · 12 min read
Bifrost is the open-source AI gateway from Maxim AI: a Go binary that routes model traffic across providers behind one OpenAI-compatible API, with a Model Context Protocol (MCP) gateway built into the same process. The picks in this roundup have matching features, each with its own strengths and weaknesses. Some take directory-resolved access further with agent-side rules, some are hosted MCP gateway products rather than tools you run, and some are older gateways handling that same routing work.
Below, we cover Bifrost’s purpose, why evaluations leave it, and how these MCP gateway and LLM gateway options stack up: Speakeasy, LiteLLM, Kong, TrueFoundry, plus Mintive (formerly MintMCP).
NOTE
We build Speakeasy, which appears in this roundup, so read us as an interested party. Claims about other vendors link to their public documentation or to comparisons we have already published, and we say so where a vendor's documentation leaves a question open.
What is Bifrost?
Bifrost, the gateway for AI from Maxim AI, is open-sourced with Apache 2.0. Applications point their SDK at a Bifrost base URL and the gateway routes each request across 20+ providers with automatic fallbacks, load balancing, and semantic caching, and its built-in MCP gateway aggregates tools at a single endpoint with per-virtual-key allow-lists and OAuth to upstream servers. Performance is the headline: Bifrost publishes benchmarks claiming microseconds of added overhead per request, numbers that are Maxim's own. A licensed Enterprise tier adds OIDC SSO, SCIM, RBAC, signed audit logs, and guardrails, and Bifrost Edge, in alpha, routes AI traffic from devices through the gateway.
Why do teams look for Bifrost alternatives?
Bifrost works for a group needing the fast self-hosted way for AI and app calls through a single binary MCP gateway. Evaluations continue for 4 things:
- A deeper governance focus. The principal on every decision is a virtual key rather than a directory identity; Enterprise syncs users from Okta or Entra via OIDC and SCIM, but agents themselves authenticate as keys. RBAC, SSO, audit logs, and guardrails all sit in the paid tier, and there is no path from an API contract to a generated, hosted, governed MCP server.
- A different architecture. Self-hosting is the draw and also the cost: your team runs the deployment, the config store, and the upgrades. Buyers who want governed MCP access as a managed, compliance-first service look at Mintive or at hybrids like Speakeasy.
- A more established LLM gateway. Bifrost's performance numbers are vendor-run benchmarks against LiteLLM, the incumbent it names. Teams that weight ecosystem maturity and integration surface over claimed latency pick LiteLLM, and enterprises already running Kong get model routing on the platform they operate.
- Agent-side enforcement. Bifrost governs at the traffic layer, and Bifrost Edge, in alpha, decides which AI apps and MCP servers a device may reach. Hooks inside coding agents that see prompts, shell commands, and file edits before they execute, approval workflows, and session-level monitoring are a different control surface, and they are where the governance platforms compete.
Which Bifrost alternative fits your MCP gateway architecture?
Each alternative fits one of the three MCP gateway architectures mapped in which MCP gateway architecture do I need: infrastructure, governance, or a hybrid that also supplies the servers.
Bifrost alternatives at a glance
Speakeasy AI Control Plane: MCP governance with directory-native identity
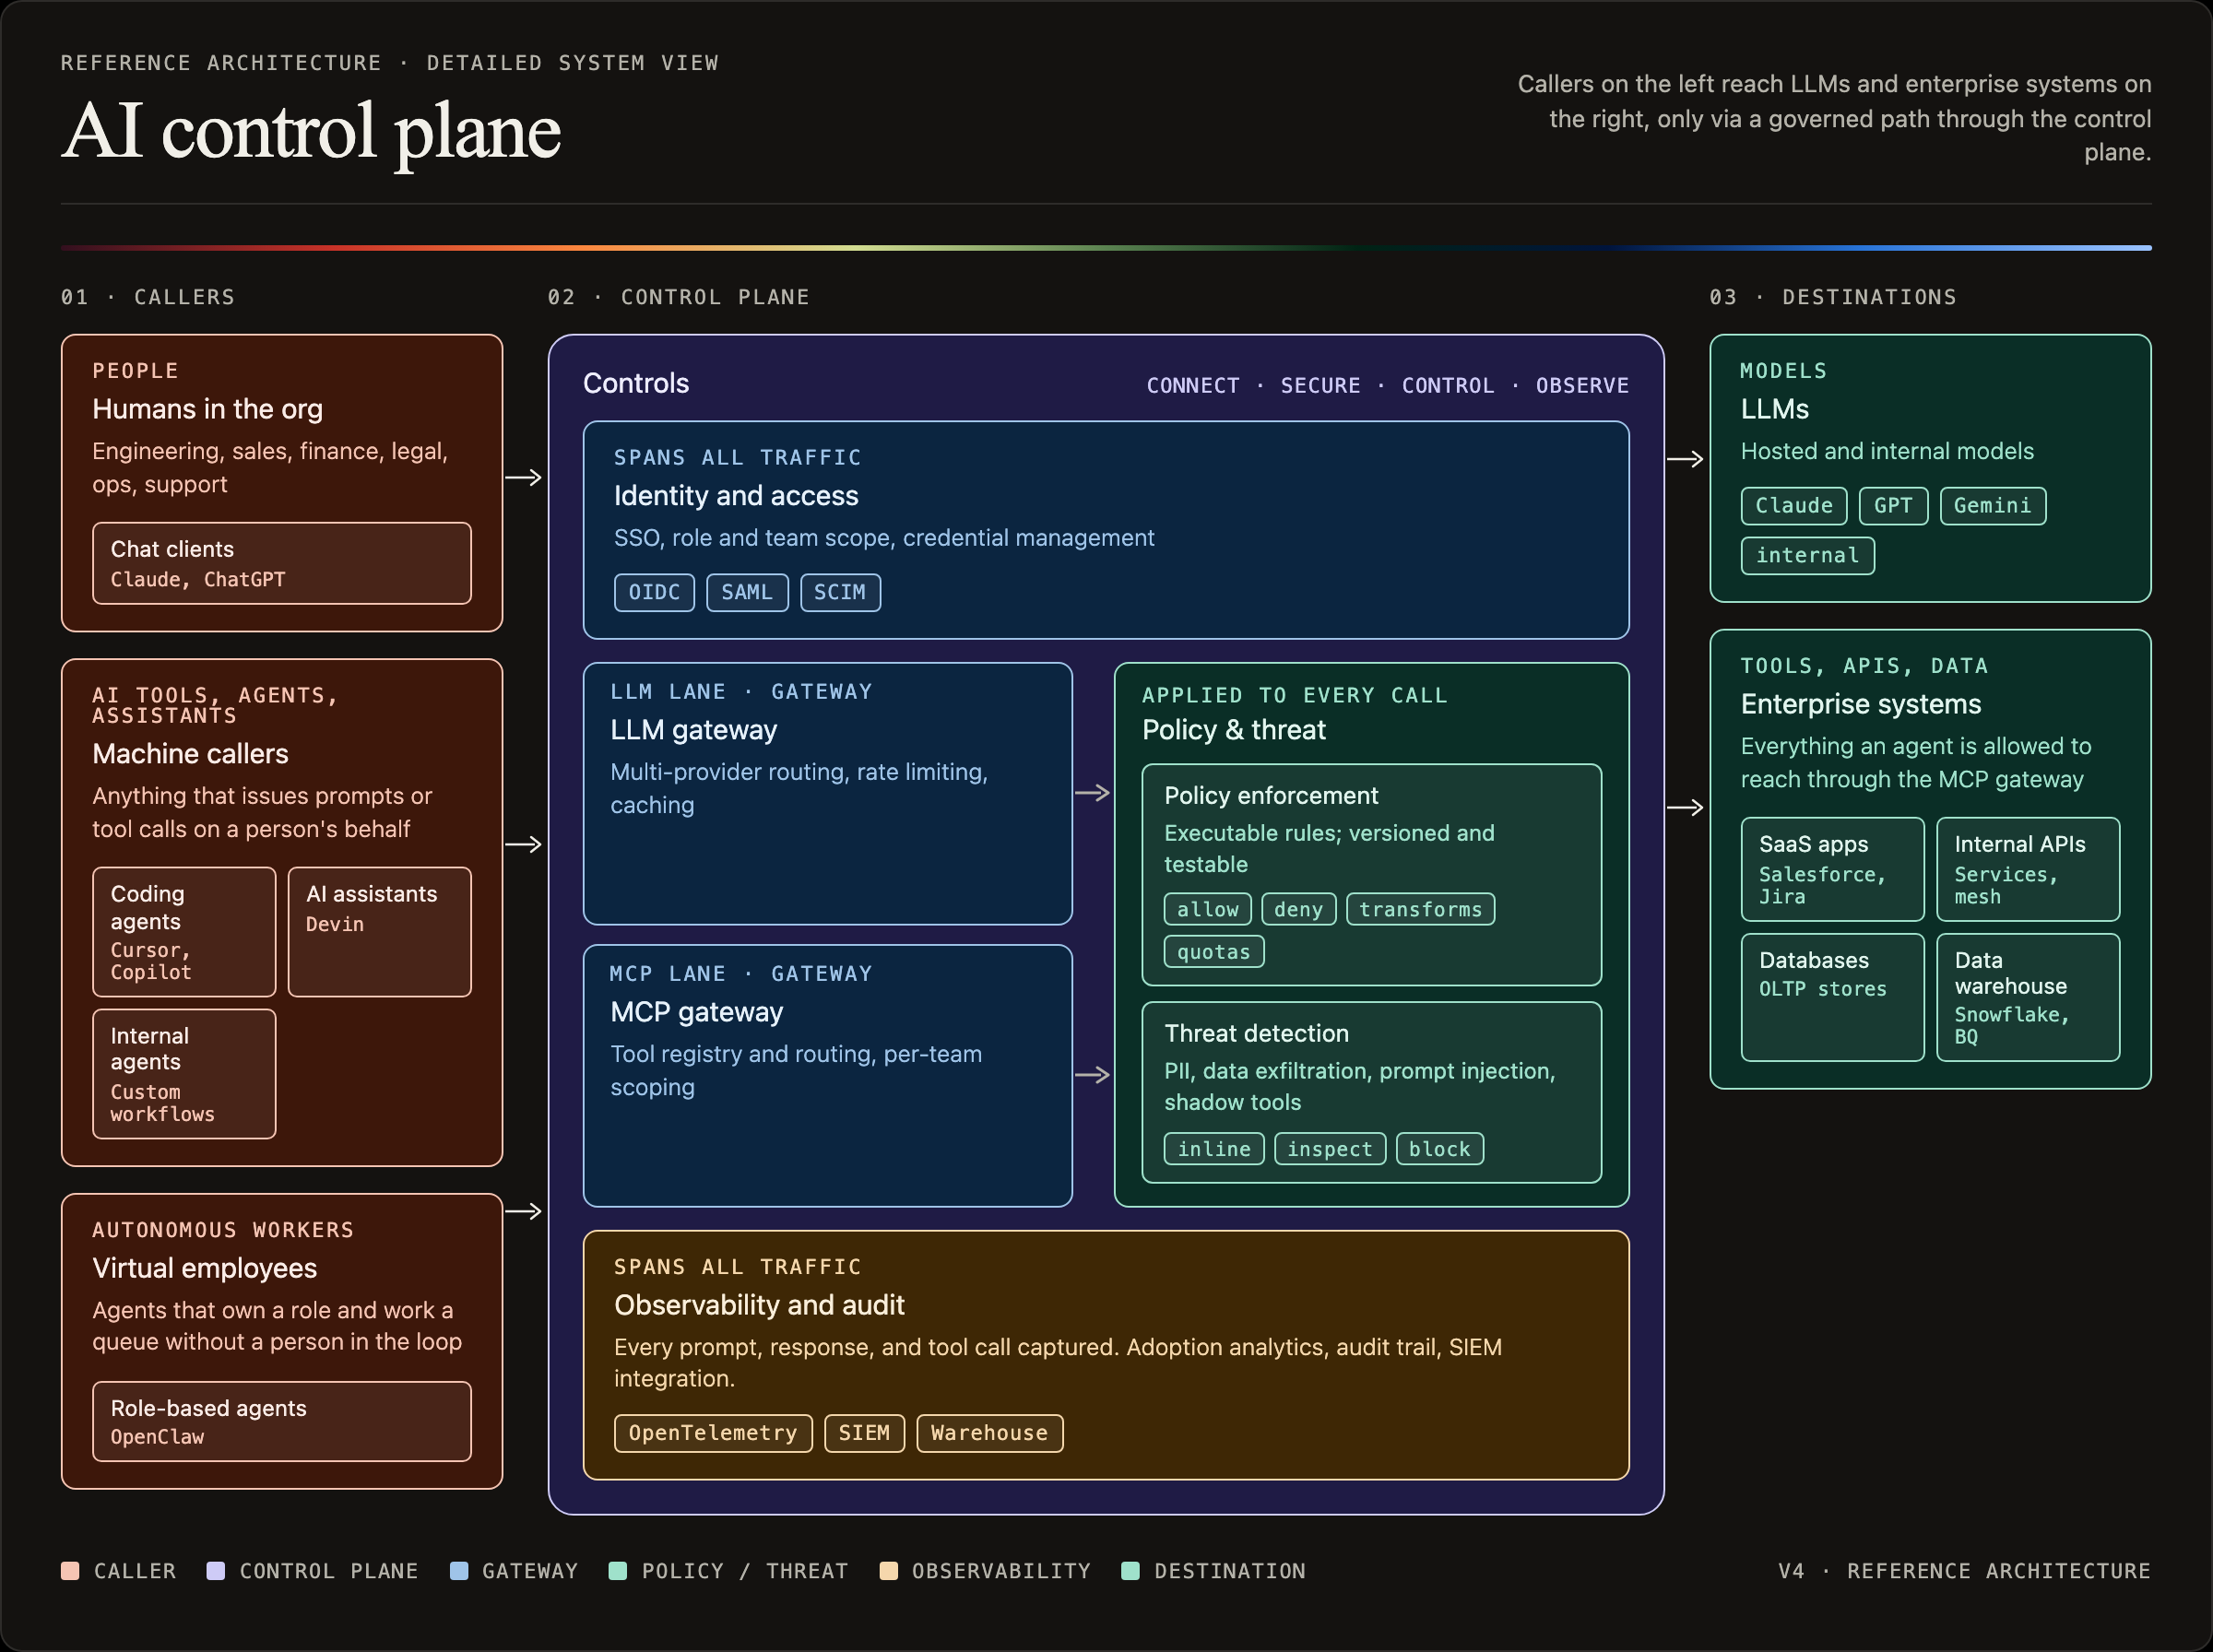
Speakeasy is the alternative when the evaluation widens from "route model and tool traffic fast" to "govern every AI surface and supply the tools our agents need." The MCP gateway is one part of an AI Control Plane that connects AI clients to tools, secures every interaction, controls who reaches what, and observes usage and cost across the organization. Identity resolves to the directory: people sync from Okta or Entra through directory sync, Agent Identity, in early access, syncs from providers such as Entra Agent ID or is created in Speakeasy, and one permission model covers both, so "who is this principal" always answers to the identity provider rather than to a virtual key.
Policy enforcement across agents and clients
You write and check the safeguards. Risk policies use opt-in LLM review for its prompt injection heuristic, while its detector catalog lists keys, bank info, PII, state identifiers across the UK, EU, US, and APAC, plus medical IDs across prompts, answers, actions, and results. Natural-language guardrails replay against recent live sessions to produce a scorecard before they enforce, and custom detection rules in CEL are tested against a real session. Enforcement reaches any MCP client through standard OAuth 2.1 authorization at the gateway, agent hooks in Claude Code, Claude Cowork, Cursor, Codex, and OpenCode, and a device agent on macOS, Windows, and Linux. Your existing API rules create MCP instances and run them under the same control. Speakeasy does not have an LLM routing gateway. For failover, groups leave a gateway such as Bifrost or LiteLLM in the chain, or add one LiteLLM integration to put a pre-call guardrail in place. Speakeasy holds SOC 2 Type 2 and ISO 27001, and the line-by-line version is Speakeasy vs Bifrost.
LiteLLM: the established LLM gateway Bifrost benchmarks against
LiteLLM is the incumbent in Bifrost's own marketing, so it belongs at the top of any alternatives list. It is a Python-based, open-source proxy exposing one OpenAI-compatible API for more than 100 services, with retries, fallbacks, account tokens, and per-key and per-team budgets included. Its MCP gateway extends the proxy to tool traffic, with OAuth 2.0 to upstream servers, access controlled by key, team, and organization, and spend tracked per MCP server. A guardrails framework runs providers such as Presidio, Lakera, Bedrock, and Azure Content Safety, and a Generic Guardrail API accepts a control plane of your choosing, the hook the Speakeasy LiteLLM integration uses. It self-hosts anywhere, including air-gapped, and its enterprise page lists SOC 2 Type 2 and ISO 27001, with SSO, SCIM, and audit logs in the paid tier. Maxim advertises the catch with Bifrost: Bifrost's vendor-run benchmarks claim large latency advantages we haven't verified, while LiteLLM's counterweight comes from ecosystem maturity plus wider connections. If you moved on from Bifrost over reasons besides speed, those same architectural issues, key-based sign-in plus license-gated business tools, matter here too.
Kong: API gateway with MCP support and semantic caching
Since Kong handles this through API control, businesses already on Kong get an option without another gateway. Its AI gateway extends the platform they use for API traffic to model traffic, routing requests across LLM providers through one API with semantic caching, prompt guards, and token-based rate limiting. The Kong MCP Registry, in Tech Preview inside Kong Konnect, pairs a server catalog with the AI gateway for runtime enforcement. Kong wins on operational convenience: business backing, an established plugin ecosystem, and a single vendor for API, model, and MCP calls. The caution is MCP maturity while it remains in preview, and API-management tools have historically been better at linking and routing traffic than governing access.
TrueFoundry: enterprise AI gateway with built-in governance
For Bifrost’s setup, TrueFoundry remains the nearest business analogue. Its AI gateway routes application traffic across more than 250 LLMs with load balancing, failover, semantic caching, and budget controls. An MCP gateway extends the same infrastructure with governance built in: RBAC and policy support, plus a guardrails framework that orchestrates providers like AWS Bedrock and Azure PII Detection. This service deploys to SaaS or self-hosted on Kubernetes, including air-gapped setups, fitting groups that need Bifrost’s routing work with vendor backing. Logs remain gated for the Enterprise tier, which the pricing page shows. Since TrueFoundry runs nothing locally, it cannot see data that bypasses its gateway. See Speakeasy vs TrueFoundry for the full comparison.
Mintive: managed MCP gateway for agent governance and compliance
If operations made you leave Bifrost, use Mintive. It is an enterprise MCP gateway delivered as a managed service: hosted connectors Mintive operates, a self-serve MCP store employees reach after SSO, and an endpoint product called Agent Monitor that hooks coding agents on laptops, including GitHub Copilot CLI. Its trust center shows HIPAA, CASA Tier 2, and SOC 2 Type 2. The trade-offs run opposite to Bifrost's: there is no LLM routing gateway, agent identities are native to Mintive rather than provisioned in Okta or Entra, and the most expressive policy layer is customer-authored JavaScript middleware. See Speakeasy vs Mintive for the full comparison.
What is Bifrost?
Why do teams look for Bifrost alternatives?
What are the best Bifrost alternatives?
Is Speakeasy a Bifrost alternative?
Bifrost vs Speakeasy: what is the main difference?
Which Bifrost alternative includes an LLM gateway?
Which Bifrost alternatives can self-host?
Got a point about the roundup, or believe we made a mistake? Talk with our team.
Last updated on