Slack
Connect Slack with a prefilled app manifest and all MCP permissions selected by default, with optional access restrictions.
Use an internal Slack app in the workspace you want to connect. You need permission to create or manage the app and any required workspace-admin approval. Sign in to Slack’s app settings with that account. Each connecting user authorizes access with their own Slack account; this setup does not use a bot token or a personal API key.
Slack permits internal apps and apps published in the Slack Marketplace. Unlisted distributed apps cannot use its MCP server. If your app restricts allowed IP addresses, ask your network administrator to include the Control Plane’s outbound addresses. Do not remove the restriction.
Choose Automatic setup for a new app, or Manual setup to configure an existing app. Both paths end with copying the app credentials into the Control Plane. You only need to complete one path.
Automatic setup (recommended)
Create your Slack app
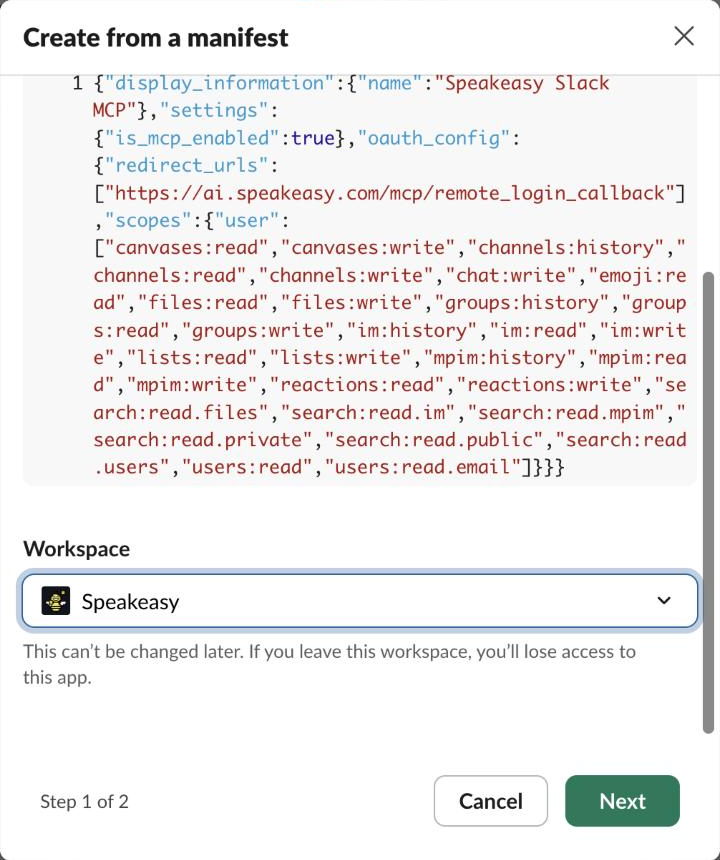
Create a new app with MCP enabled, the deployment callback registered, and all 30 supported user scopes included. No JSON entry or manual configuration is needed.
- Click Create app in Slack, select your workspace, and review the app.
- Create the app. Continue to Copy the app credentials. You do not need to complete manual setup.
The default includes all 30 read, search, and write scopes. To limit access, remove unneeded scopes from the manifest before creating the app. Tools that need those scopes will be unavailable. Use the same restricted set when connecting the credentials. Workspace approval and each user’s existing access restrictions still apply.
Manual setup
Use this alternative if you already have an internal Slack app or cannot use the automatic creation link. Do not repeat it after automatic setup.
Show manual setup instructions
Create an app from JSON
For a new app, select From a manifest in Slack’s app settings. Select the workspace, paste the JSON below, review it, and create the app. Then continue to Copy the app credentials; the JSON already sets MCP, user scopes, and the callback.
If you are configuring an existing app, skip the JSON and start at Enable MCP access.
View the full app manifest (30 user scopes)
{ "display_information": { "name": "Speakeasy Slack MCP" }, "settings": { "is_mcp_enabled": true }, "oauth_config": { "redirect_urls": [ "https://ai.speakeasy.com/mcp/remote_login_callback" ], "scopes": { "user": [ "canvases:read", "canvases:write", "channels:history", "channels:read", "channels:write", "chat:write", "emoji:read", "files:read", "files:write", "groups:history", "groups:read", "groups:write", "im:history", "im:read", "im:write", "lists:read", "lists:write", "mpim:history", "mpim:read", "mpim:write", "reactions:read", "reactions:write", "search:read.files", "search:read.im", "search:read.mpim", "search:read.private", "search:read.public", "search:read.users", "users:read", "users:read.email" ] } }}If the callback placeholder has not been filled in, replace it with your deployment’s OAuth callback URL before creating the app. You can remove scopes you do not need, but keep the same scope set in the Control Plane.
Enable MCP access for an existing app
For an existing app, complete these three configuration steps.
- Open the app in Slack’s app settings.
- Select Agents in the sidebar.
- Turn Slack Model Context Protocol (MCP) Server On.
Set user permissions for an existing app
- Select OAuth & Permissions and find Scopes.
- Add the 30 scopes in the manifest above to the user-token scopes, not the bot-token scopes. To limit access, use only the scopes for the tools you need, from Slack’s tool-to-scope table.
- Use the same selected scopes in the Control Plane.
Changing access in the Control Plane does not update an app already created in Slack. Update the app’s scopes in Slack too, then complete any required reinstallation, approval, or user authorization before using the new permissions.
Register the callback for an existing app
- On OAuth & Permissions, find Redirect URLs.
- Add
https://ai.speakeasy.com/mcp/remote_login_callbackand save.
Finish app setup
Complete this step after either automatic or manual setup.
Copy the app credentials
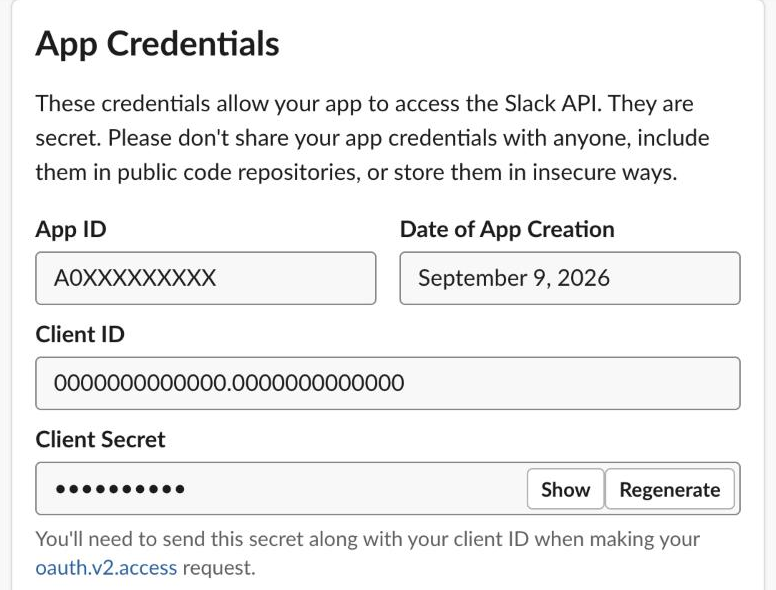
- In the Slack app, open Basic Information and find App Credentials.
- Copy Client ID and Client Secret for the Control Plane identity settings. Reveal the secret if needed. Do not share it in chat, screenshots, or source control.
- Save the configuration in the Control Plane.
Use these client credentials, not the App ID or a bearer token. No app configuration token is needed for the prefilled creation link.
Connect in the Control Plane
Add the server in Speakeasy
-
In the sidebar, under MCP Gateway, select MCP and click Add new.
-
Choose Hosted remotely. In MCP server URL, enter:
https://mcp.slack.com/mcp -
Optionally enter a display name. Leave User session issuer at its default and click Verify connectivity.
-
Keep User Identity selected. If Guardrails appears, leave it off. Click Save.
The server stays Disabled until you finish identity setup. Open its Settings > Identity to configure the app credentials.
Connect your credentials
-
Create or configure the Slack app. The prefilled creation link already sets MCP access, all 30 user scopes, and the callback. Do not repeat those settings in Slack.
-
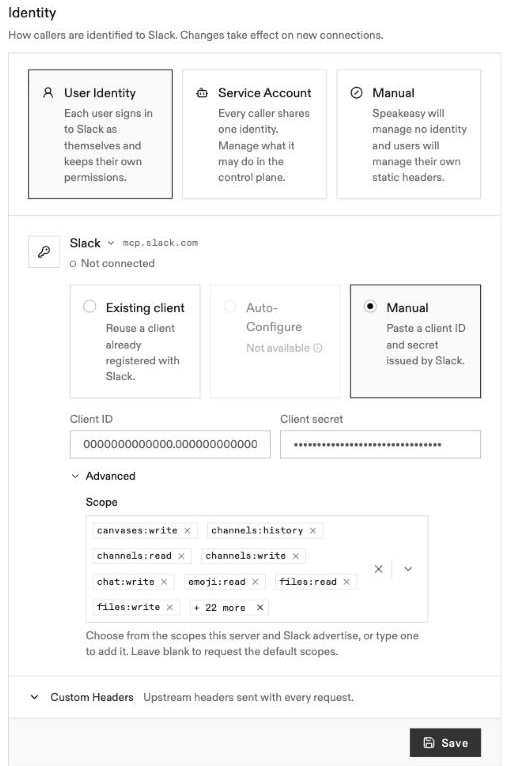
Under Identity, select User Identity. In Choose an identity provider, confirm Slack’s issuer,
https://mcp.slack.com, is selected. It is badged Will be created if the project has no Slack provider yet. -
Choose Manual. Paste the Client ID and Client Secret. Slack requires the secret even if the field says Optional.
-
Open Advanced and open the Scope dropdown. Select the exact user scopes configured on the Slack app. For the full prefilled manifest, select all 30 scopes in the list.
If you removed permissions in Slack, leave the same scopes unselected here. Do not leave Scope blank or select permissions that the app does not grant.
-
Click Save and confirm with Save changes if asked.
-
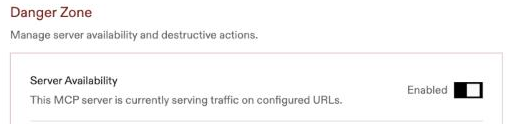
In Settings > Danger Zone > Server Availability, turn on Enable MCP server.
When a person first uses the server, Slack asks them to authorize access with their own account. Saving client credentials does not grant anyone access to Slack data. If you change scopes after creating the app, update them in both Slack and the Control Plane, then complete any required approval or authorization.
This guide covers setup only. For anything beyond it — billing, tool behavior, limits — see Slack’s MCP documentation.